NET::ERR_CERT_COMMON_NAME_INVALID: 4 Easy Ways to Fix It
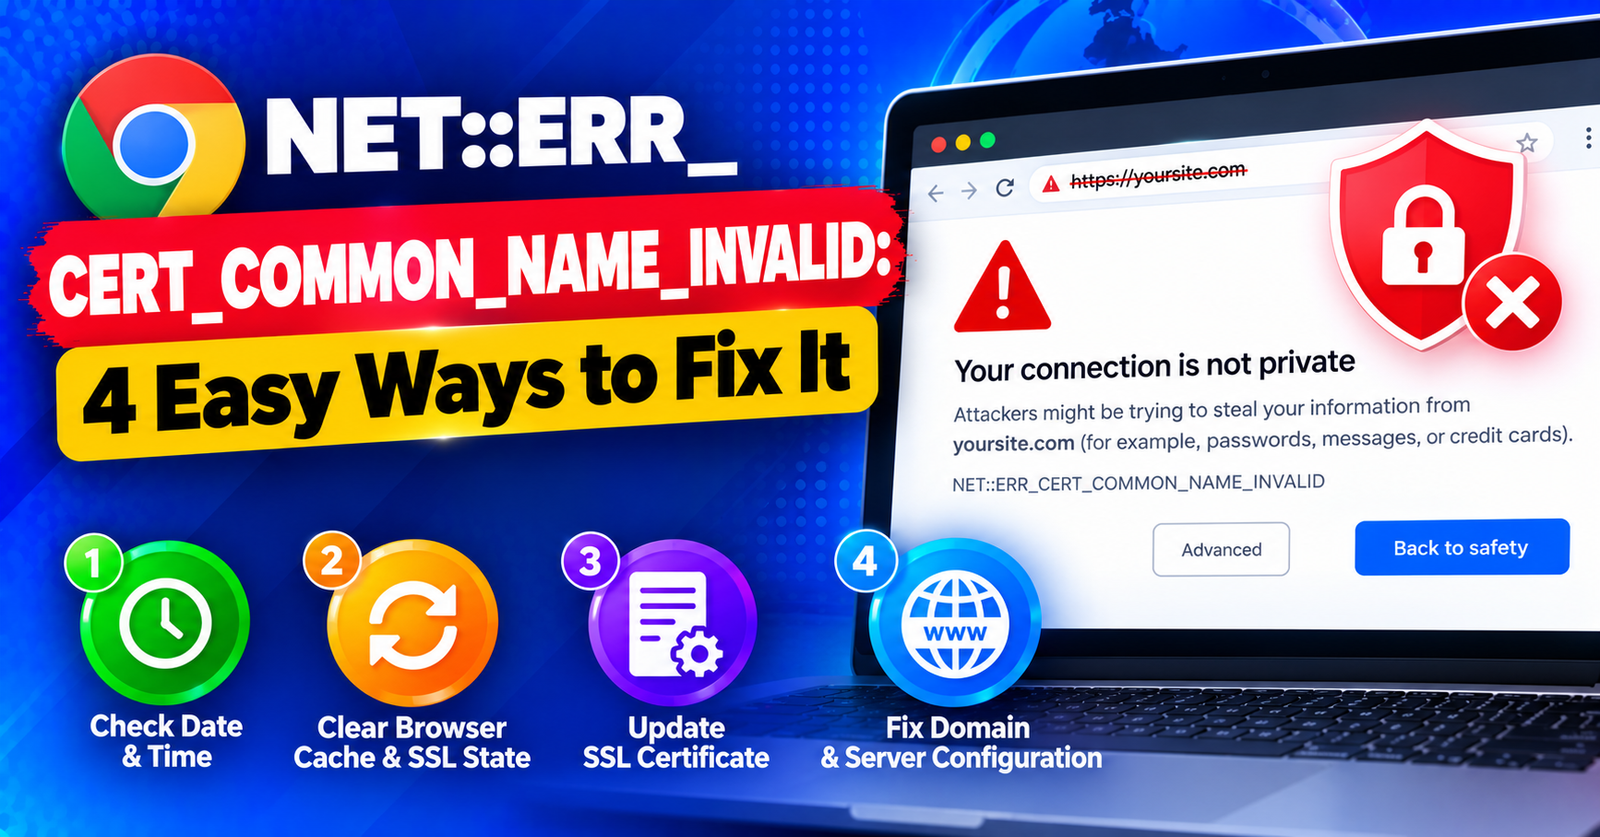
You visit a website, expecting to read an article, and Chrome suddenly blocks your screen with a massive red warning sign:
Your connection is not private / NET::ERR_CERT_COMMON_NAME_INVALID
This error occurs when the domain name listed inside an SSL certificate does not match the actual domain name currently in your browser’s address bar.
Because attackers sometimes attempt to use a valid certificate from a different site to spoof secure connections, modern browsers actively block the connection to protect user data from phishing.
In this guide, we will explain the root causes of the net err cert common name invalid error and show you how to fix it whether you are a visitor or the website owner.
What Causes NET::ERR_CERT_COMMON_NAME_INVALID?
Every SSL certificate contains a Common Name (CN) or a list of Subject Alternative Names (SAN) specifying which domains the certificate covers.
The mismatch error is typically triggered by:
- WWW vs. Non-WWW Mismatch: The certificate was issued only for
domain.com, but the visitor typedwww.domain.com(or vice versa). - Shared Web Hosting Default Certificate: The server served the hosting company’s default shared SSL instead of your custom domain certificate.
- Third-Party CDN Misconfiguration: A CDN (like Cloudflare) not having your custom subdomains included in its universal SSL bundle.
- Antivirus HTTPS Interception: Local antivirus software presenting its own untrusted certificate.
Fix 1: Check WWW and Non-WWW Redirects (For Website Owners)
The most common cause of this error on new websites is a missing 301 redirect between www and non-www URLs.
If your SSL certificate only protects yourdomain.com, anyone typing https://www.yourdomain.com will see the Common Name Invalid warning.
How to fix in .htaccess:
Add a clean 301 redirect to enforce the version covered by your certificate:
RewriteEngine On
RewriteCond %{HTTP_HOST} ^www\.(.*)$ [NC]
RewriteRule ^(.*)$ https://%1/$1 [R=301,L]
This automatically redirects any incoming www traffic to your secure non-www address.
Fix 2: Re-issue Your SSL Certificate with Wildcard or SAN Support
When generating an SSL certificate (via cPanel Let’s Encrypt or AutoSSL), ensure both domain variants are checked:
- Log in to cPanel and open SSL/TLS Status.
- Locate your domain and check both
yourdomain.comandwww.yourdomain.com. - Click Run AutoSSL.
AutoSSL will generate a single certificate covering both forms of your domain name.
Fix 3: Clear the Windows SSL State and Chrome DNS Cache (For Visitors)
If the website owner recently fixed their certificate but your browser still displays the old mismatch error, clearing your cached certificates is required.
- Press Windows Key + R, type
inetcpl.cpl, and press Enter. - Go to the Content tab.
- Click Clear SSL state.
- In Google Chrome, navigate to
chrome://net-internals/#dnsand click Clear host cache.
Fix 4: Temporarily Bypass the Warning (Advanced)
If you are a developer testing a local staging site or intranet server where a self-signed certificate mismatch is expected, you can bypass the warning screen in Chrome:
Simply click anywhere on the white warning page and type on your keyboard:
thisisunsafe
Chrome will immediately bypass the certificate validation lock and load the webpage. (Use this strictly for development purposes!)
For more web and server troubleshooting tutorials, check out our guides on fixing the failed to write file to disk error and resolving 413 request entity too large issues.
Wrapping Up
The NET::ERR_CERT_COMMON_NAME_INVALID warning occurs whenever an SSL certificate fails to list the exact domain requested. Ensuring proper 301 redirects and issuing certificates that include both www and non-www versions resolves the mismatch permanently.
Did configuring your redirects fix the issue? Let us know in the comments below!